Confidly
EU-built anonymous whistleblowing channel from Confidly OU (Estonia), self-serve from EUR 39/month, EU-hosted with AI-assisted investigation.
This vendor applies AI or machine learning to whistleblower reports (for example speech-to-text, summarisation, severity or category classification, drafting replies, or machine translation). Automated processing of disclosures can bring the deployment within scope of the EU AI Act and can route sensitive personal data through a third-party inference provider. Confirm the model provider, its data-retention terms, and whether report content can be excluded before relying on it. Vendor detail: AI summarises reports, classifies severity, suggests categories, translates 25+ languages, and drafts acknowledgement replies; all suggestions advisory and human-confirmed. Inference via AWS Bedrock eu-central-1 (Frankfurt), stated zero data retention.
Rubric score
42 / 50
Evidence tier P
Public pages only. No reporter submission or handler environment was reviewed.
Score and evidence for each criterion
fully meets · partly meets · does not meet, or not verified
Legal compliance 12 / 16
- Local transposition law referenced with article numbers Score: 1 of 2. Names national transposition laws (HinSchG, Loi Sapin II, D.lgs 24/2023, Ley 2/2023, Wbk and others) but article-level mapping within those statutes was not shown
- Directive 2019/1937 Article 2(1) categories in intake Score: 1 of 2. Country-specific intake templates and AI category suggestion are disclosed, but explicit Directive Article 2(1) category coverage was not verified
- Anonymous reporting default-on or equal-status Score: 2 of 2. Anonymous reporting is the default by design (no IP, email, or device fingerprint; case code plus 6-digit secret)
- 7-day acknowledgment + 3-month feedback deadline tracking Score: 2 of 2. Automatic reporter status updates at 7 days and 3 months, mapped to Directive Article 9, are documented
- Configurable retention with automatic deletion Score: 1 of 2. Configurable per-channel retention (Enterprise) and one-click erasure are disclosed, but scheduled automatic deletion was not verified
- Report register / log Score: 1 of 2. Append-only audit log and filterable case list are disclosed; a separate formal report register was not verified
- Append-only handler audit trail Score: 2 of 2. Append-only, hash-chained audit log on every action (submission, assignment, status, AI suggestion) is documented
- DPA + DPIA support documented Score: 2 of 2. Public Article 28 DPA with SCCs and a pre-filled Article 35 DPIA template are both documented
Reporter experience 9 / 10
- Web form, mobile-responsive, with file upload Score: 2 of 2. Web reporting form with audio, video, and document attachments (metadata-stripped) is documented; mobile-first WhatsApp and SMS intake also stated
- Two-factor reporter access (Case ID + passcode) Score: 2 of 2. Reporter return access uses a case code plus a 6-digit bcrypt-hashed secret
- Two-way anonymous communication Score: 2 of 2. Two-way anonymous chat with the reporter is documented
- Structured intake aligned to Article 2(1) Score: 1 of 2. Country-specific structured intake and AI classification are disclosed, but Directive Article 2 alignment was not verified
- Reporter form in local language Score: 2 of 2. Six pre-translated form languages (EN, DE, FR, IT, ES, NL) plus AI handling of 25+ languages are documented
Handler experience 10 / 10
- Case management dashboard with status workflow Score: 2 of 2. Case dashboard with named status workflow (received, under review, investigating, resolved) is documented
- Assign cases to handlers (rotation or multi-handler) Score: 2 of 2. Investigator assignment, role-based assignment, auto-escalation, and external ombudsperson seats are documented
- Deadline reminder notifications Score: 2 of 2. Auto-escalation of unassigned high-severity cases beyond 24h and 7-day/3-month reporter updates are documented
- Internal notes (not visible to reporter) Score: 2 of 2. Internal notes hidden from the reporter are documented
- Role-based access control (≥3 roles) Score: 2 of 2. Role-based access with four roles (admin, manager, investigator, auditor) is documented
Security and trust 5 / 8
- ISO 27001 certified Score: 0 of 2. Vendor is not ISO 27001 certified; the trust page lists ISO 27001 as in progress (Stage 1 targeted Q1 2027). Hetzner hosting is hoster-level, not a vendor product certification
- No EOL software components Score: 1 of 2. Public pages did not expose enough implementation detail to independently verify the absence of EOL components
- EU data residency with country disclosed Score: 2 of 2. EU data residency is disclosed with country named: production data in Hetzner Falkenstein, Germany
- Sub-processor list + right to object Score: 2 of 2. A public sub-processor list is documented with 30-day advance notice and a stated right to object
Commercial 6 / 6
- Published pricing Score: 2 of 2. All three standard tiers publish prices (Starter EUR 39, Pro EUR 124, Enterprise EUR 332 per month billed annually); only 10,000+ employees is quote-only
- Free trial available (self-serve) Score: 2 of 2. A 14-day free trial with no credit card and self-serve signup is documented
- Monthly contract option Score: 2 of 2. Monthly billing is offered alongside annual billing
Facts
- Headquarters
- Tallinn, Estonia
- Hosting
- Hetzner Online GmbH, Falkenstein, Germany (vendor-stated)
- Pricing
- Starter EUR 39/month billed annually (EUR 468/year, up to 100 employees); Pro EUR 124/month billed annually (EUR 1,488/year, 100-500 employees); Enterprise EUR 332/month billed annually (EUR 3,984/year, up to 2,000 employees / 5 channels). Monthly billing also offered; annual billing stated to save roughly 17%.Priced by total employee headcount, not per user. All plans include a 14-day free trial (full Pro features, no credit card). Prices are EUR plus VAT, reverse-charged for EU B2B. 10,000+ employees, on-prem, or custom integrations are quote-only via sales.
- Languages on reporting form
- 25
- Founded
- 2026
- Ownership
- Private, Confidly OU (Estonia)
- Product scope
- Standalone whistleblower product
Measured, not published
Established by checking the vendor's own infrastructure rather than by reading its marketing. Every figure here can be reproduced from the links given.
- DMARC policy
- Enforced (quarantine)
- DNSSEC
- Unsigned
- Legal entity
- Confidly OÜ VAT EE10XXXXXXXX · imprint
Capabilities
- Anonymous reporting ✓
- Multi-channel intake ✓
- Public API ✓
- Free trial ✓
- Two-factor authentication ✓
- Audit log —
- EU Directive 2019/1937 (vendor claim) ✓
✓ published by the vendor · ✗ vendor states it is not offered · — not published either way
Certifications and national law
Certifications
None published
National laws referenced
- EU Directive 2019/1937
- Germany (HinSchG)
- France (Loi Sapin II)
- Italy (D.lgs 24/2023)
- Spain (Ley 2/2023)
- Netherlands (Wbk)
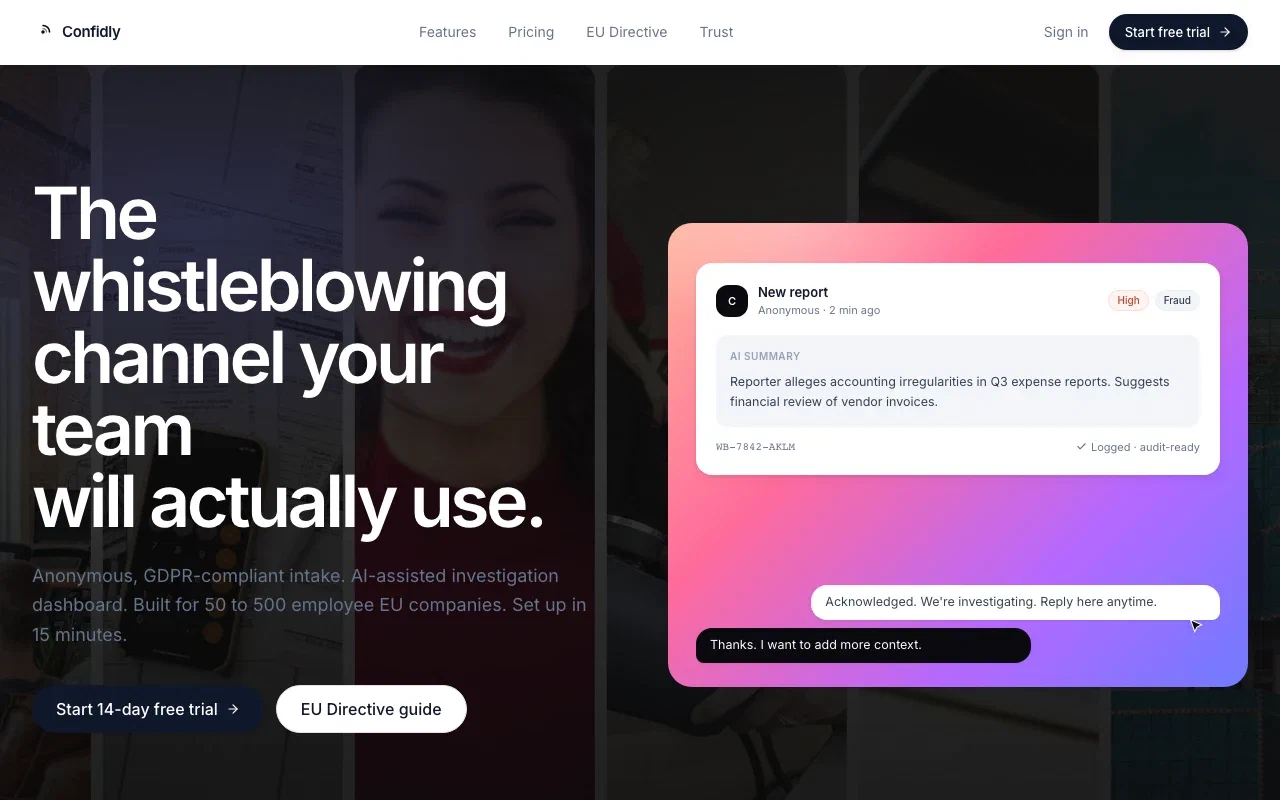
EU companies of roughly 50 to 500 employees wanting a focused, self-serve, Directive-compliant whistleblowing channel with anonymous intake and AI-assisted case handling, without a full GRC suite.
Distinctive features
- Published self-serve pricing across three tiers with a 14-day free trial and no credit card
- Anonymous-by-design intake (no IP, email, or device fingerprint; reporter gets a case code plus 6-digit secret)
- EU data residency named (Hetzner Falkenstein, Germany) with a public sub-processor list and 30-day objection window
- Automatic reporter status updates at 7 days and 3 months mapped to Directive Article 9
- Append-only, hash-chained audit log exportable as CSV or JSON for regulator inspection
- Country-specific intake templates referencing named national transposition laws across all 27 EU states plus EEA and UK
Add-ons and conditions
Costs or terms not included in the headline price.
- Pricing is banded by total employee headcount, not per user; crossing a band moves you to the next tier
- ISO 27001 and SOC 2 Type II are listed as in progress, not certified, on public pages reviewed
- REST API, webhooks, SCIM, BYOK encryption, and configurable per-channel retention are Enterprise-only
- AI classification and translation (beyond summaries) plus SSO require the Pro tier or higher
- The public imprint reviewed lists Confidly OU in Tallinn but shows registry and VAT numbers as placeholders
- Handler sign-in is delegated to Clerk (clerk.com), a US identity provider, so authentication and session identity are processed outside the EU even though report data is EU-hosted
- Vendor social links (LinkedIn, GitHub, X) were broken on the pages reviewed
Notable
- Operated by Confidly OU, a private limited company registered in the Estonian Business Register with a registered office in Tallinn, Estonia; the site footer states the product is built in Helsinki and hosted in the EU.
- Positioned as a focused, self-serve whistleblowing channel for EU companies of roughly 50 to 500 employees, deliberately narrower than a full GRC or compliance suite.
- Reporter intake is anonymous by design: no account, no IP, no email, and no device fingerprint; the reporter receives a case code plus a 6-digit secret (stated to be stored only in hashed form) for two-way anonymous follow-up.
- Multiple intake channels are documented: web form, audio and video attachments, and mobile-first WhatsApp and SMS intake, plus printable QR-code posters in six EU languages.
- AI features (Pro and Enterprise) summarise reports, classify severity, suggest categories, translate 25+ languages, and draft acknowledgement replies; all AI output is stated to be advisory and human-confirmed. Inference runs on AWS Bedrock eu-central-1 (Frankfurt) with stated zero data retention.
- Compliance features include automatic reporter status updates at 7 days and 3 months (mapped to Directive Article 9), an append-only hash-chained audit log exportable as CSV or JSON, and an auto-generated country-tailored annual compliance report.
- The trust page states EU data residency with production data in Hetzner Falkenstein, Germany, TLS 1.3 and AES-256 encryption, a public sub-processor list with a 30-day objection window, and an annual third-party penetration test (summary under NDA).
- Handler authentication is delegated to Clerk (clerk.com), a US-based identity platform: report data is EU-hosted, but sign-in and session identity run through a US sub-processor, a cross-border transfer consideration under GDPR Chapter V.
- ISO 27001 and SOC 2 Type II are listed as in progress with target dates; ISO 27701 and TISAX are planned or on request. No certification was verified as complete on the public pages reviewed.
- Public legal artifacts include an Article 28 DPA with SCCs, a privacy policy, a pre-filled Article 35 DPIA template, and a RoPA entry; some pen-test, TIA, and BCP documents are stated to be available only under NDA.
- Pricing is published for all three standard tiers, banded by total employee headcount rather than per user, with a 14-day free trial (no credit card) and both monthly and annual billing. Deployments above 2,000 employees, on-prem, or custom integrations are handled via sales.
- The public imprint lists Confidly OU in Tallinn but shows the registry number and VAT identification number as placeholders as of the reviewed date; the stated supervisory authority is the Estonian Data Protection Inspectorate (AKI).
Frequently asked questions about Confidly
Answers derived from vendor-published materials dated on this page.
Is Confidly suitable for SMEs under 250 employees?
Which national whistleblower laws does Confidly explicitly reference?
Does Confidly process whistleblower report content with AI?
Similar to Confidly
Other platforms in the directory with overlapping pricing model, certifications, or procurement path.
 TrueSpeak
Italian-run multi-locale whistleblowing SaaS with published per-plan pricing from €19/month and a locale site for each of eight markets.
 Disclosurely
UK anonymous-reporting and case-management SaaS with Pro at GBP 39.99/month, a 14-day trial, and published security limitations.
 Firmsys
Czech whistleblowing channel from SPWeb s.r.o. with fixed monthly tiers from 590 Kc and web plus automated telephone reporting.
 Heimdal
Swedish whistleblowing system from Heimdal Systems AB, free for organizations under 50 employees and EUR 499/year above that.
Sources and verification
Every fact on this page comes from Confidly's own published materials. These are the pages that were read, and the date they were read.
- Last verified
8 of the vendor pages cited below has changed since this entry was verified. What this means
Cited pages last re-fetched
- confidly.eu/ (opens in new tab)
- confidly.eu/features (opens in new tab)
- confidly.eu/pricing (opens in new tab)
- confidly.eu/trust (opens in new tab)
- confidly.eu/eu-directive (opens in new tab)
- confidly.eu/legal/imprint (opens in new tab)
- confidly.eu/legal/dpa (opens in new tab)
- confidly.eu/legal/privacy (opens in new tab)